Blog
Web Security
I write about securing web apps in practice: Content Security Policy with Helmet in Express, JWT authentication, and verifying Shopify webhook signatures. For developers who want concrete, correct implementations of common security controls.
Node2Shell: Node.js Brotli RCE and the Fix
Node2Shell (CVE-2026-111497) is a Node.js Brotli RCE flaw. See which Express paths are exposed and the fixed versions.
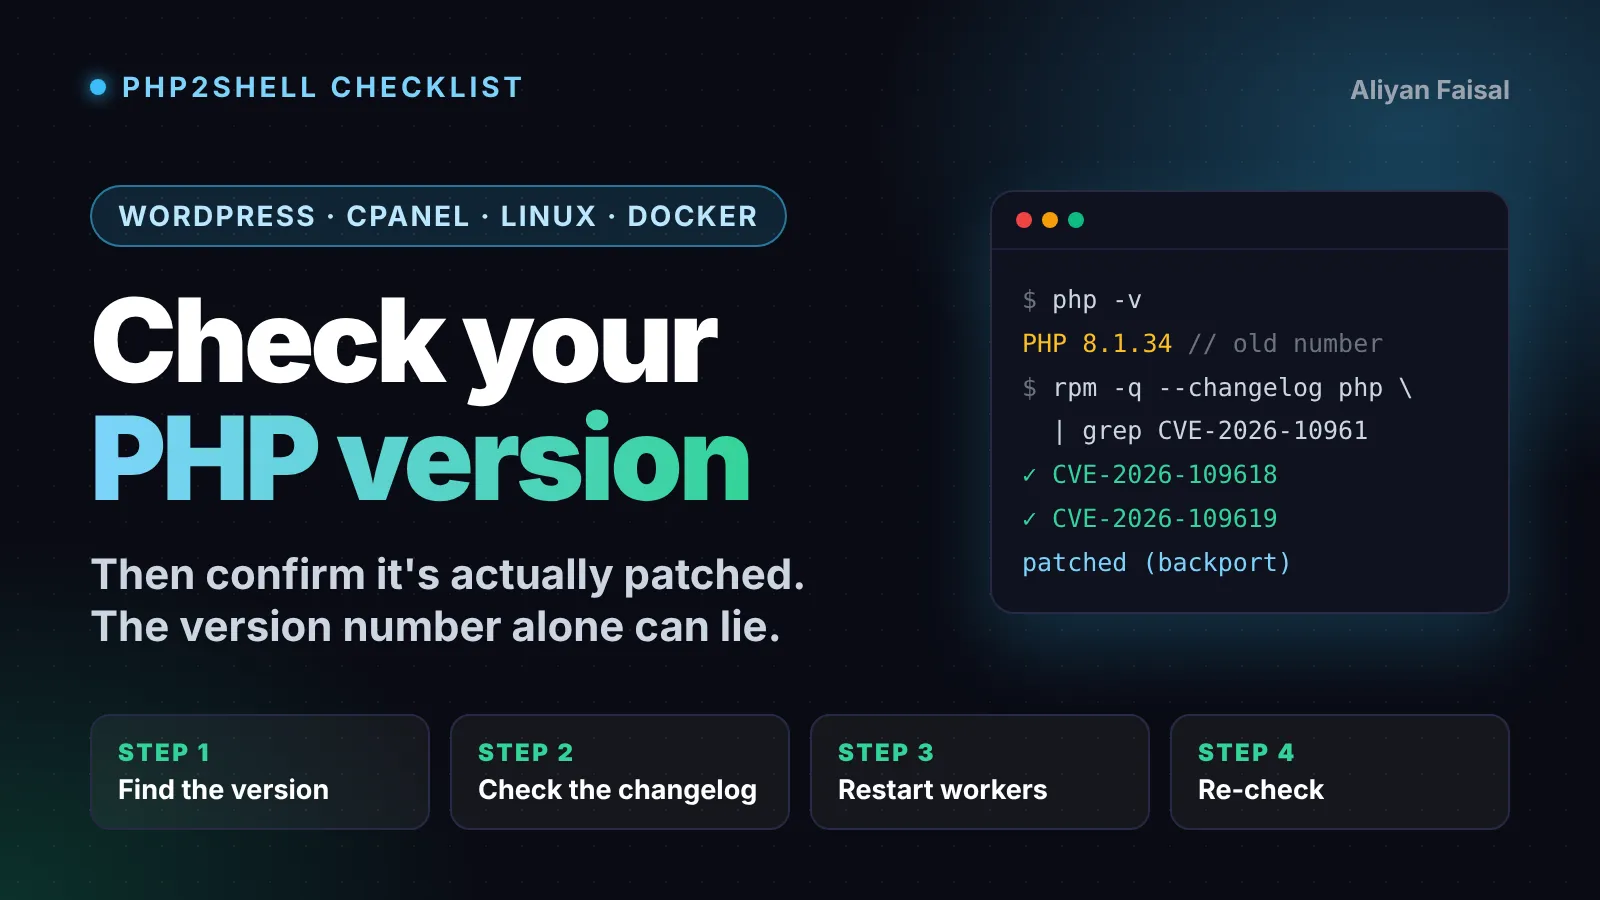
How to Check Your PHP Version After PHP2Shell
How to check your PHP version and confirm it's patched against PHP2Shell on WordPress, cPanel, Linux and Docker.
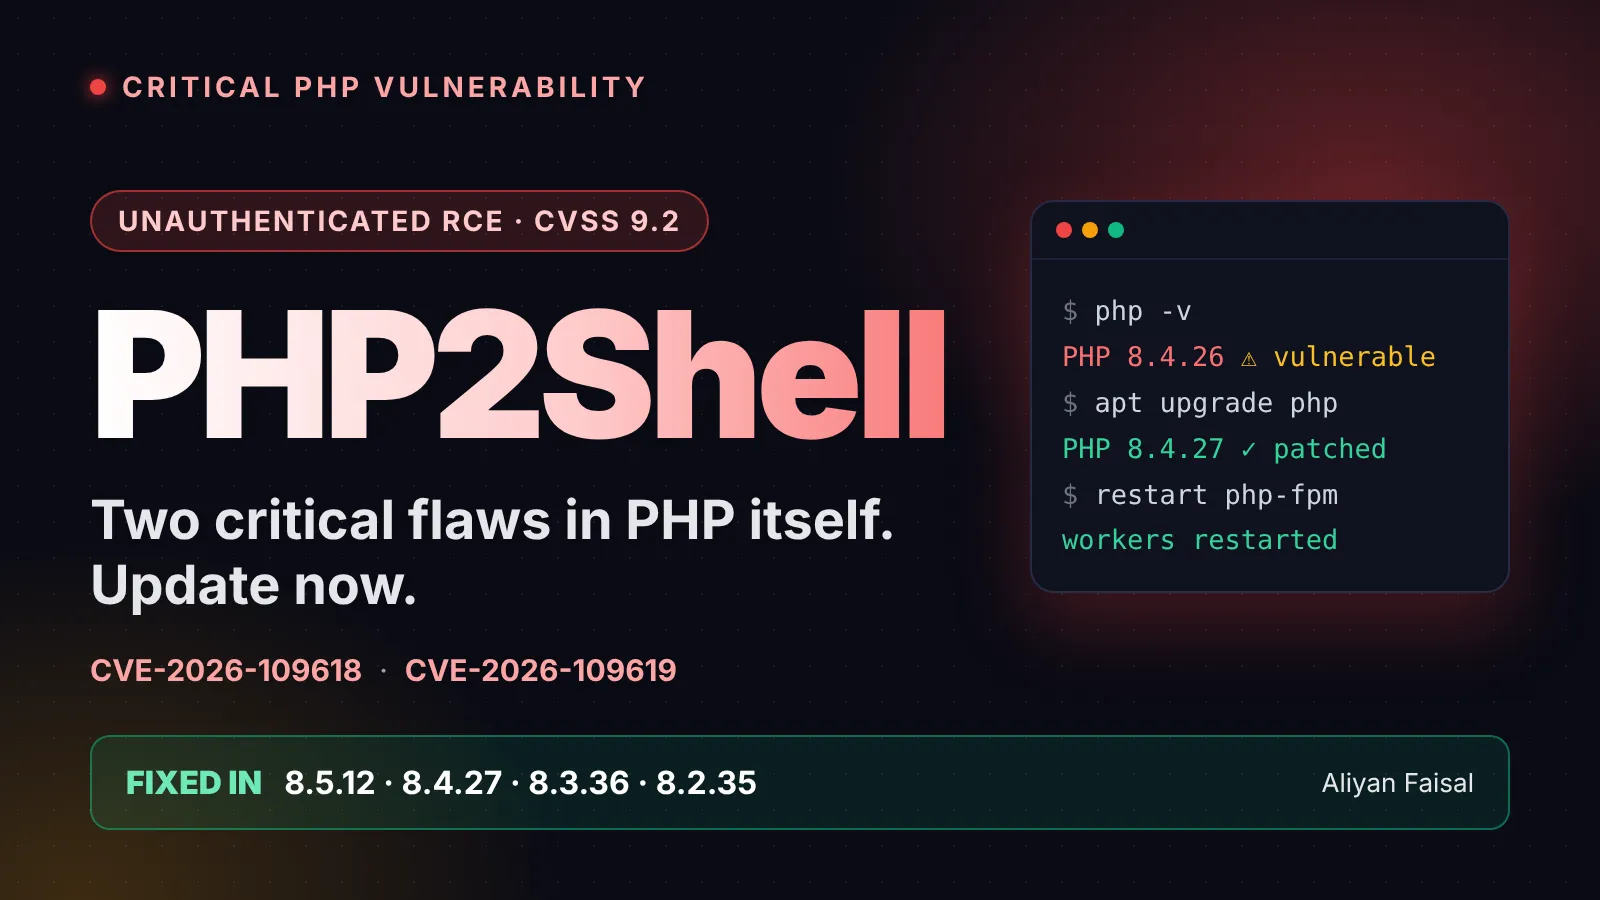
PHP2Shell: Critical PHP RCE Flaws and the Fix
PHP2Shell explained: two critical PHP flaws allow remote code execution. Fixed versions, developer steps and an owner checklist.
Fix Laravel 419 CSRF Token Mismatch Error
A real fix for the Laravel 419 CSRF token mismatch error — session cookie settings, SPA/Axios setup, and when to actually use the except array.
Content Security Policy in Express With Helmet
Learn how to set up a Content Security Policy in Express with Helmet: nonces, report-only rollout, and the mistakes that weaken your XSS defense.